
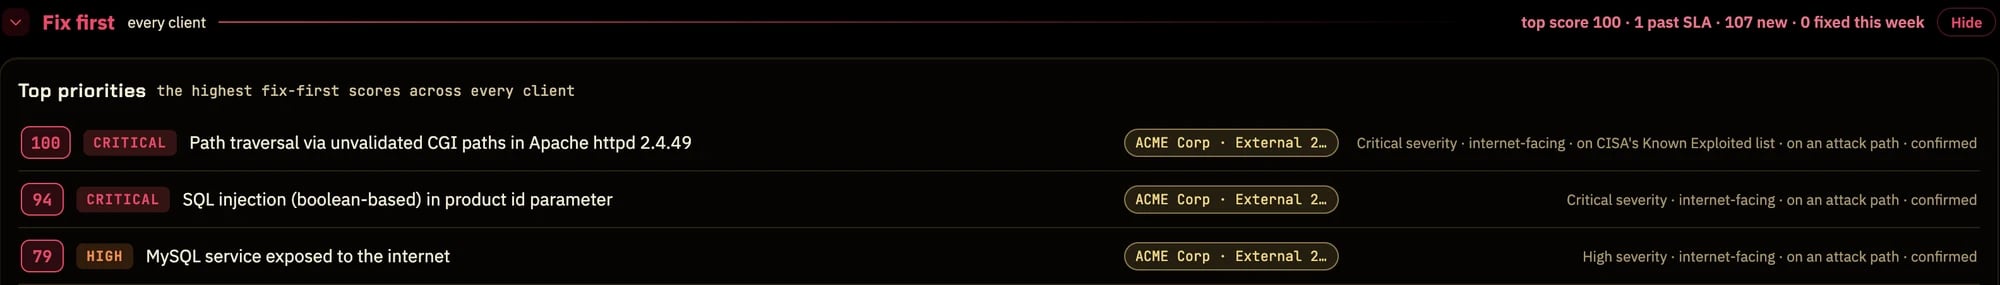
Top priorities on the Command Center: the highest fix-first scores across every client, each with its project and reasons
How the score is built
The score starts from the issue’s severity and adds points for each thing that makes it more urgent. It is capped at 100.
Informational notes score 0 and stay out of the ranking.
Two examples from the same engagement: a high-severity issue that is internet-facing, on CISA’s list, on an attack path and confirmed scores 100. A critical issue on an internal host that is on an attack path and confirmed scores 79. Priority is not severity: the high comes first.
What the colours mean
Where you see it
Project dashboard
A Top priorities card lists the project’s highest-scoring open issues, each with its score, risk, title and reasons, one click to the issue.
Issues list
Every open issue carries its score as a small badge before the title (hover it for the reasons). Turn on Fix first order above the list to rank every issue by score instead of grouping by severity. The choice is remembered in your browser.
Command Center
The Fix first band brings the highest scores from every client into one ranked list, each row tagged with its project. See The Command Center.
Synapse portal
Clients see Highest risk first on their dashboard, built only from what they can already see. See below.
The Known Exploited list
The KEV signal uses CISA’s full Known Exploited Vulnerabilities catalogue, kept on your D0pam1ne server and refreshed once a day by the scheduler (the same download that feeds Vuln Intel). A fresh install fetches it within a minute of starting. Scoring itself never makes a network call: it reads the local copy, so if the server is offline for a day the last copy simply stands.What clients see
In the Synapse portal, a client’s Highest risk first list uses the same score with one difference: the attack-path part is left out. Attack paths are your team’s analysis of how an attacker would move through the client’s systems, and they are kept out of everything the client sees, the same as the client report. So a client’s ranking is built from severity, internet exposure, CISA’s list and CVSS, and the reasons never mention attack paths. Only issues already reported to the client and still open are ranked. Their order can differ slightly from your team’s for that reason. See The client portal.The score is guidance for ordering the work. It never changes an issue’s status, severity or deadline.