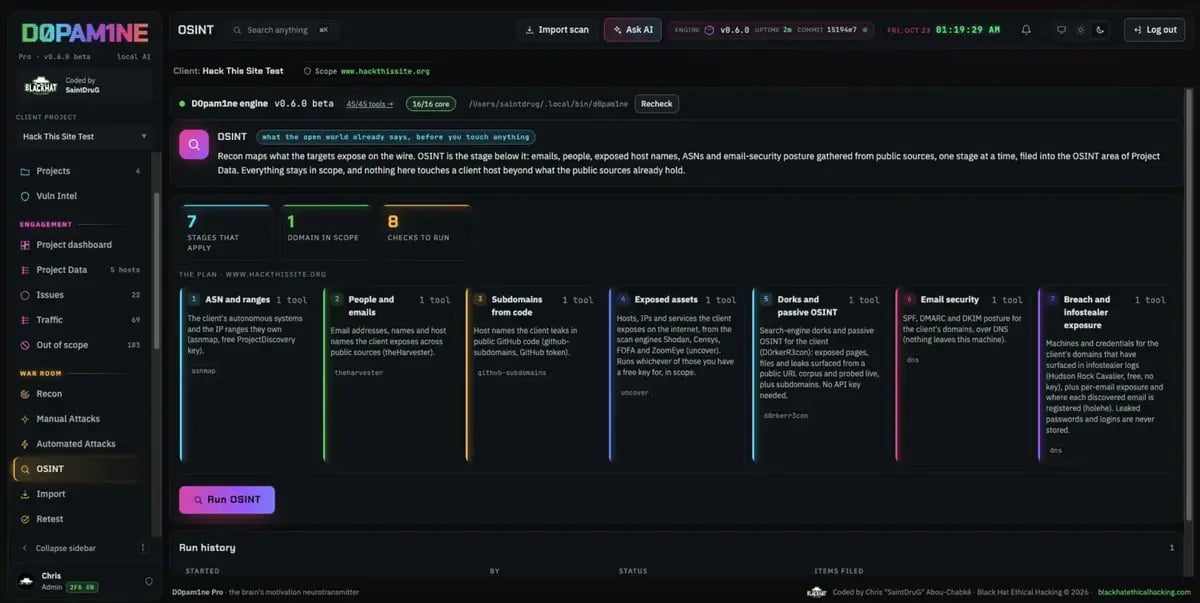
The OSINT plan: stages, tools and what each needs
The stages
Each stage runs only if its tool is installed (or runs in-process), and lists itself as skipped otherwise.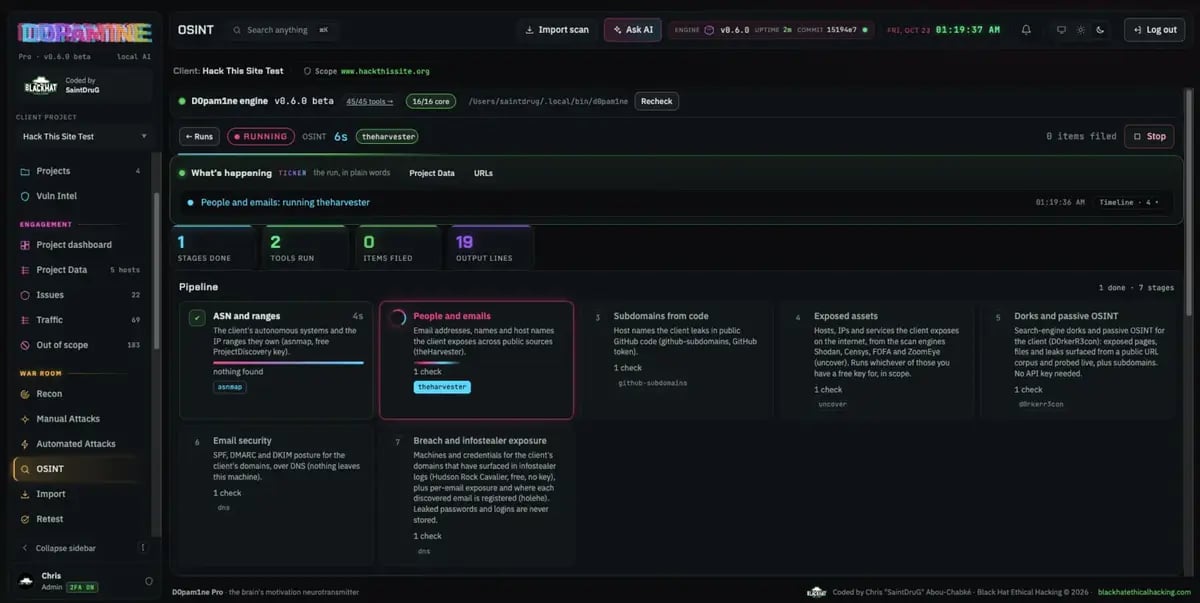
OSINT running, streaming results
Private and keyless where it counts
- Email security runs entirely in-process over DNS: nothing leaves your machine.
- Breach and infostealer exposure uses Hudson Rock’s keyless Cavalier API and
holehe; leaked passwords and logins are never stored. - The people and emails stage queries long-standing public sources only.
Running it
Start OSINT and the pipeline runs stage by stage, streaming items filed and output lines, exactly like recon and attacks. Results land in Project Data’s OSINT tab, where you can flag items and carry them into a report.OSINT is a Pro feature and works from your in-scope domains. Add the optional API keys under Settings to reach more sources; without them, the keyless stages still run.