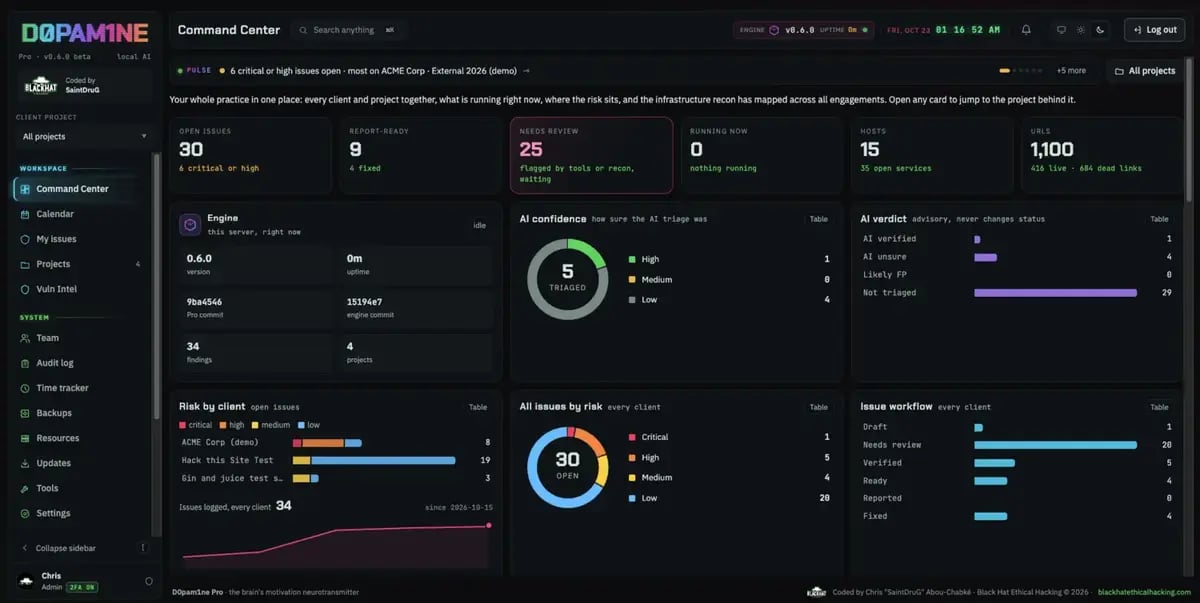
The Command Center: every client and project in one view
Key components
The engine
The open-source core. A single registry drives the recon and OSINT toolchain, phase by phase, from subdomains and ports to live web, crawling, content discovery, parameters and secrets. Driven by the
d0pam1ne CLI, or by Pro.D0pam1ne Pro
The self-hosted web app: the War Room where recon, Manual and Automated Attacks, OSINT, Project Data, triage and reporting live. Multi-user, role-based, 2FA, with everything on infrastructure you control.
Local AI
An on-device model run by Ollama. Triage, report drafting and the Ask AI assistant run locally: no cloud, no account, no telemetry. Your project data never leaves the machine.
The pipeline
Every engagement moves through the same pipeline. Each stage feeds the next, and everything lands in one project.1
Scope
Define the client and what is in scope. Recon and attacks act only inside it, and anything out of scope is logged, never probed. See Client and scope.
2
Recon
The engine maps the live attack surface: subdomains, DNS, ports, services, live web, URLs, content, parameters and secrets, with profiles for speed or stealth and an adaptive Evasive Mode.
3
OSINT
Map public exposure before you touch the target: ASNs, people and emails, exposed assets, dorks, email-security posture, breach and infostealer data. See OSINT.
4
Project Data
Everything recon and OSINT find lands in Project Data: hosts and services, the attack-surface graph, URLs, technologies, secrets and the traffic log.
5
6
Needs Review
Findings flow into Issues, where AI triage suggests a verdict and you confirm, edit or reject. Only verified issues reach the client.
7
Report
Turn verified findings into a branded PDF, interactive HTML, Markdown, JSON or Word, then retest and show what was fixed.
What sets it apart
Adaptive Evasive Mode
Not a fixed delay. D0pam1ne paces requests against how the target actually responds, backing off on rate-limiting and blocks, and can route supported tools through Tor with exit-IP rotation so no single address draws attention.
Recon that feeds attacks
Attacks are not a separate scan. Each category reads the recon signal that justifies it and builds its in-scope target lists automatically, so the right tools run against the right hosts.
Private by design
The AI runs on your machine via Ollama. No cloud model, no account, no telemetry, and D0pam1ne refuses any AI endpoint that is not local.
Client-ready reporting
One branded house design across PDF and interactive HTML, with a full per-finding anatomy (risk, impact, attacker view, evidence, remediation) and a matching retest report.
Editions
Standard
The licensed build: the full recon, attack, OSINT, triage and reporting workflow for your team.
Founder Edition
Black Hat Ethical Hacking’s in-house build, which unlocks extras such as Word (.docx) report export. Founder-only features are marked throughout these docs.
Where to go next
D0pam1ne runs entirely on infrastructure you control. Keep the port firewalled to trusted addresses, and require login and 2FA on every network interface. See the security notes before exposing it.
Who builds D0pam1ne
D0pam1ne is coded by Chris “SaintDruG” Abou-Chabké, Founder and Chief Hacking Officer at Black Hat Ethical Hacking.
Black Hat Ethical Hacking
Offensive security solutions, vulnerability assessments and digital forensics. Visit blackhatethicalhacking.com, or contact the team.